Shadowsocks vs VLESS Reality: is Shadowsocks still enough in 2026?
Shadowsocks defined getting through censorship for a decade. How it compares to VLESS Reality in 2026, where it still works, where it burns, and how to switch without changing apps.
By the VPNBaron team · Updated 2 October 2026 · 4 min read
For a decade, Shadowsocks was the answer. It defined what “getting through” meant: a lean encrypted proxy, simple to run, light on the wire, and for years invisible enough. If you learned censorship circumvention before 2020, you probably learned it on Shadowsocks. VLESS Reality is what the same ecosystem builds today, and the difference is not incremental. Here’s the honest comparison.
Head to head
| Shadowsocks | VLESS Reality | |
|---|---|---|
| Designed | 2012, encrypted SOCKS-style proxy | 2023, Xray ecosystem |
| What the network sees | A fully-encrypted, high-entropy stream on an odd port | A genuine TLS session with a real, well-known website |
| Entropy detection | Exposed: “unidentifiable encrypted traffic” is itself a signature | Passes: the handshake and traffic shape are real TLS |
| Active probing | Exposed historically: probed servers can be confirmed and blocklisted | Survives: a probe receives the real website back |
| Overhead | Minimal | Small camouflage cost |
| Client apps | Everything, including legacy apps | The modern generation: sing-box family, V2Box, Hiddify, Clash Meta |
| Track record under pressure | Purged in waves, especially around sensitive dates | Current default in the anti-censorship ecosystem |
Why Shadowsocks started losing
Shadowsocks never pretended to be something else. It encrypted everything and hoped the result looked like nothing in particular. That worked until censors flipped the logic: traffic that looks like nothing in particular is itself suspicious. Equipment that flags fully-encrypted, high-entropy flows catches Shadowsocks without decrypting a byte, and it has been deployed aggressively since the early 2020s, with the dial turned up around sensitive dates.
The second weakness is older: a censor that suspects an address can simply connect to it and poke. Shadowsocks servers respond in ways that can be confirmed. Whole waves of servers have been identified and blocklisted this way, which is why the ecosystem’s own developers moved on.
Why VLESS Reality holds
Reality inverts the disguise. Instead of hiding as noise, it presents the genuine TLS handshake of a real website: real certificate presentation, real handshake shape, on TCP 443 like every HTTPS session on earth. SNI inspection sees a normal site. Fingerprinting sees a normal browser handshake. An active probe gets the real website back. There is no “unidentifiable traffic” to flag, because the traffic identifies as something ordinary and verifiable.
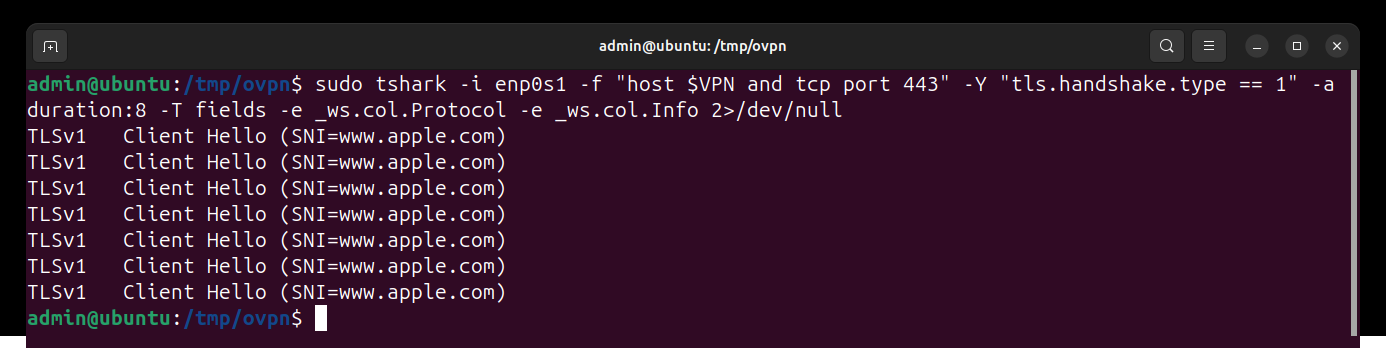
The full detection ladder, and how each rung is answered, is in What is deep packet inspection.
Migrating is smaller than you think
The client side of the ecosystem converged years ago: sing-box based apps (V2Box, Hiddify) and Clash Meta speak both protocols. If you use one of those for Shadowsocks today, switching to Reality is not a new toolchain, it’s a different subscription link.
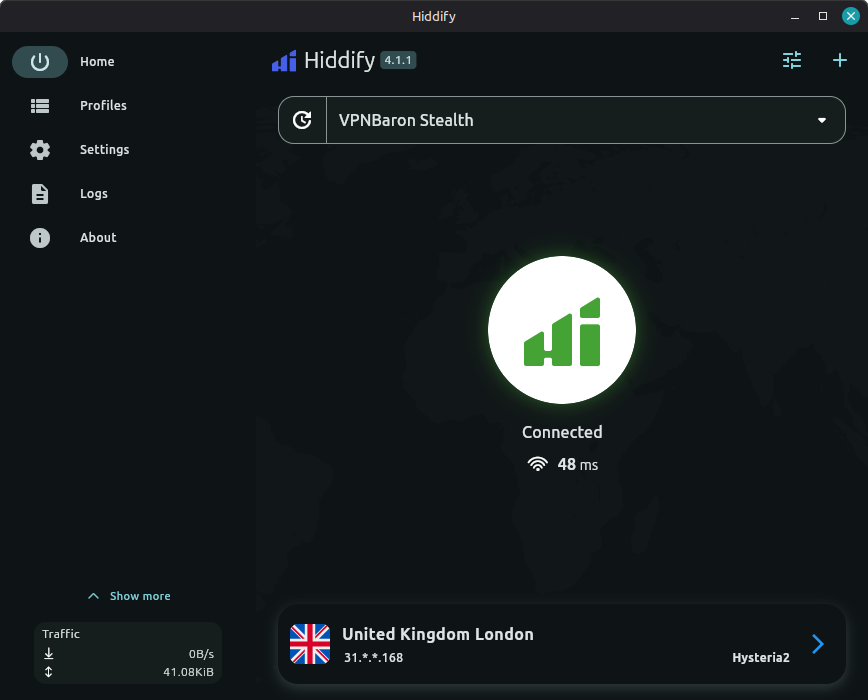
A VPNBaron stealth subscription carries VLESS Reality and Hysteria2 entries for every location: Reality for networks that inspect, Hysteria2 for speed on lossy or throttled links. Import guides: V2Box (iOS, macOS, Android) and Hiddify (Windows, Linux). Choosing between the two: Hysteria2 vs VLESS Reality.
If you run your own Shadowsocks box
Self-hosting made sense when Shadowsocks was invisible. Today it means one IP address that burns the moment it’s noticed, a disguise you maintain by hand, and you as the on-call admin during exactly the crackdowns when you need the connection most.
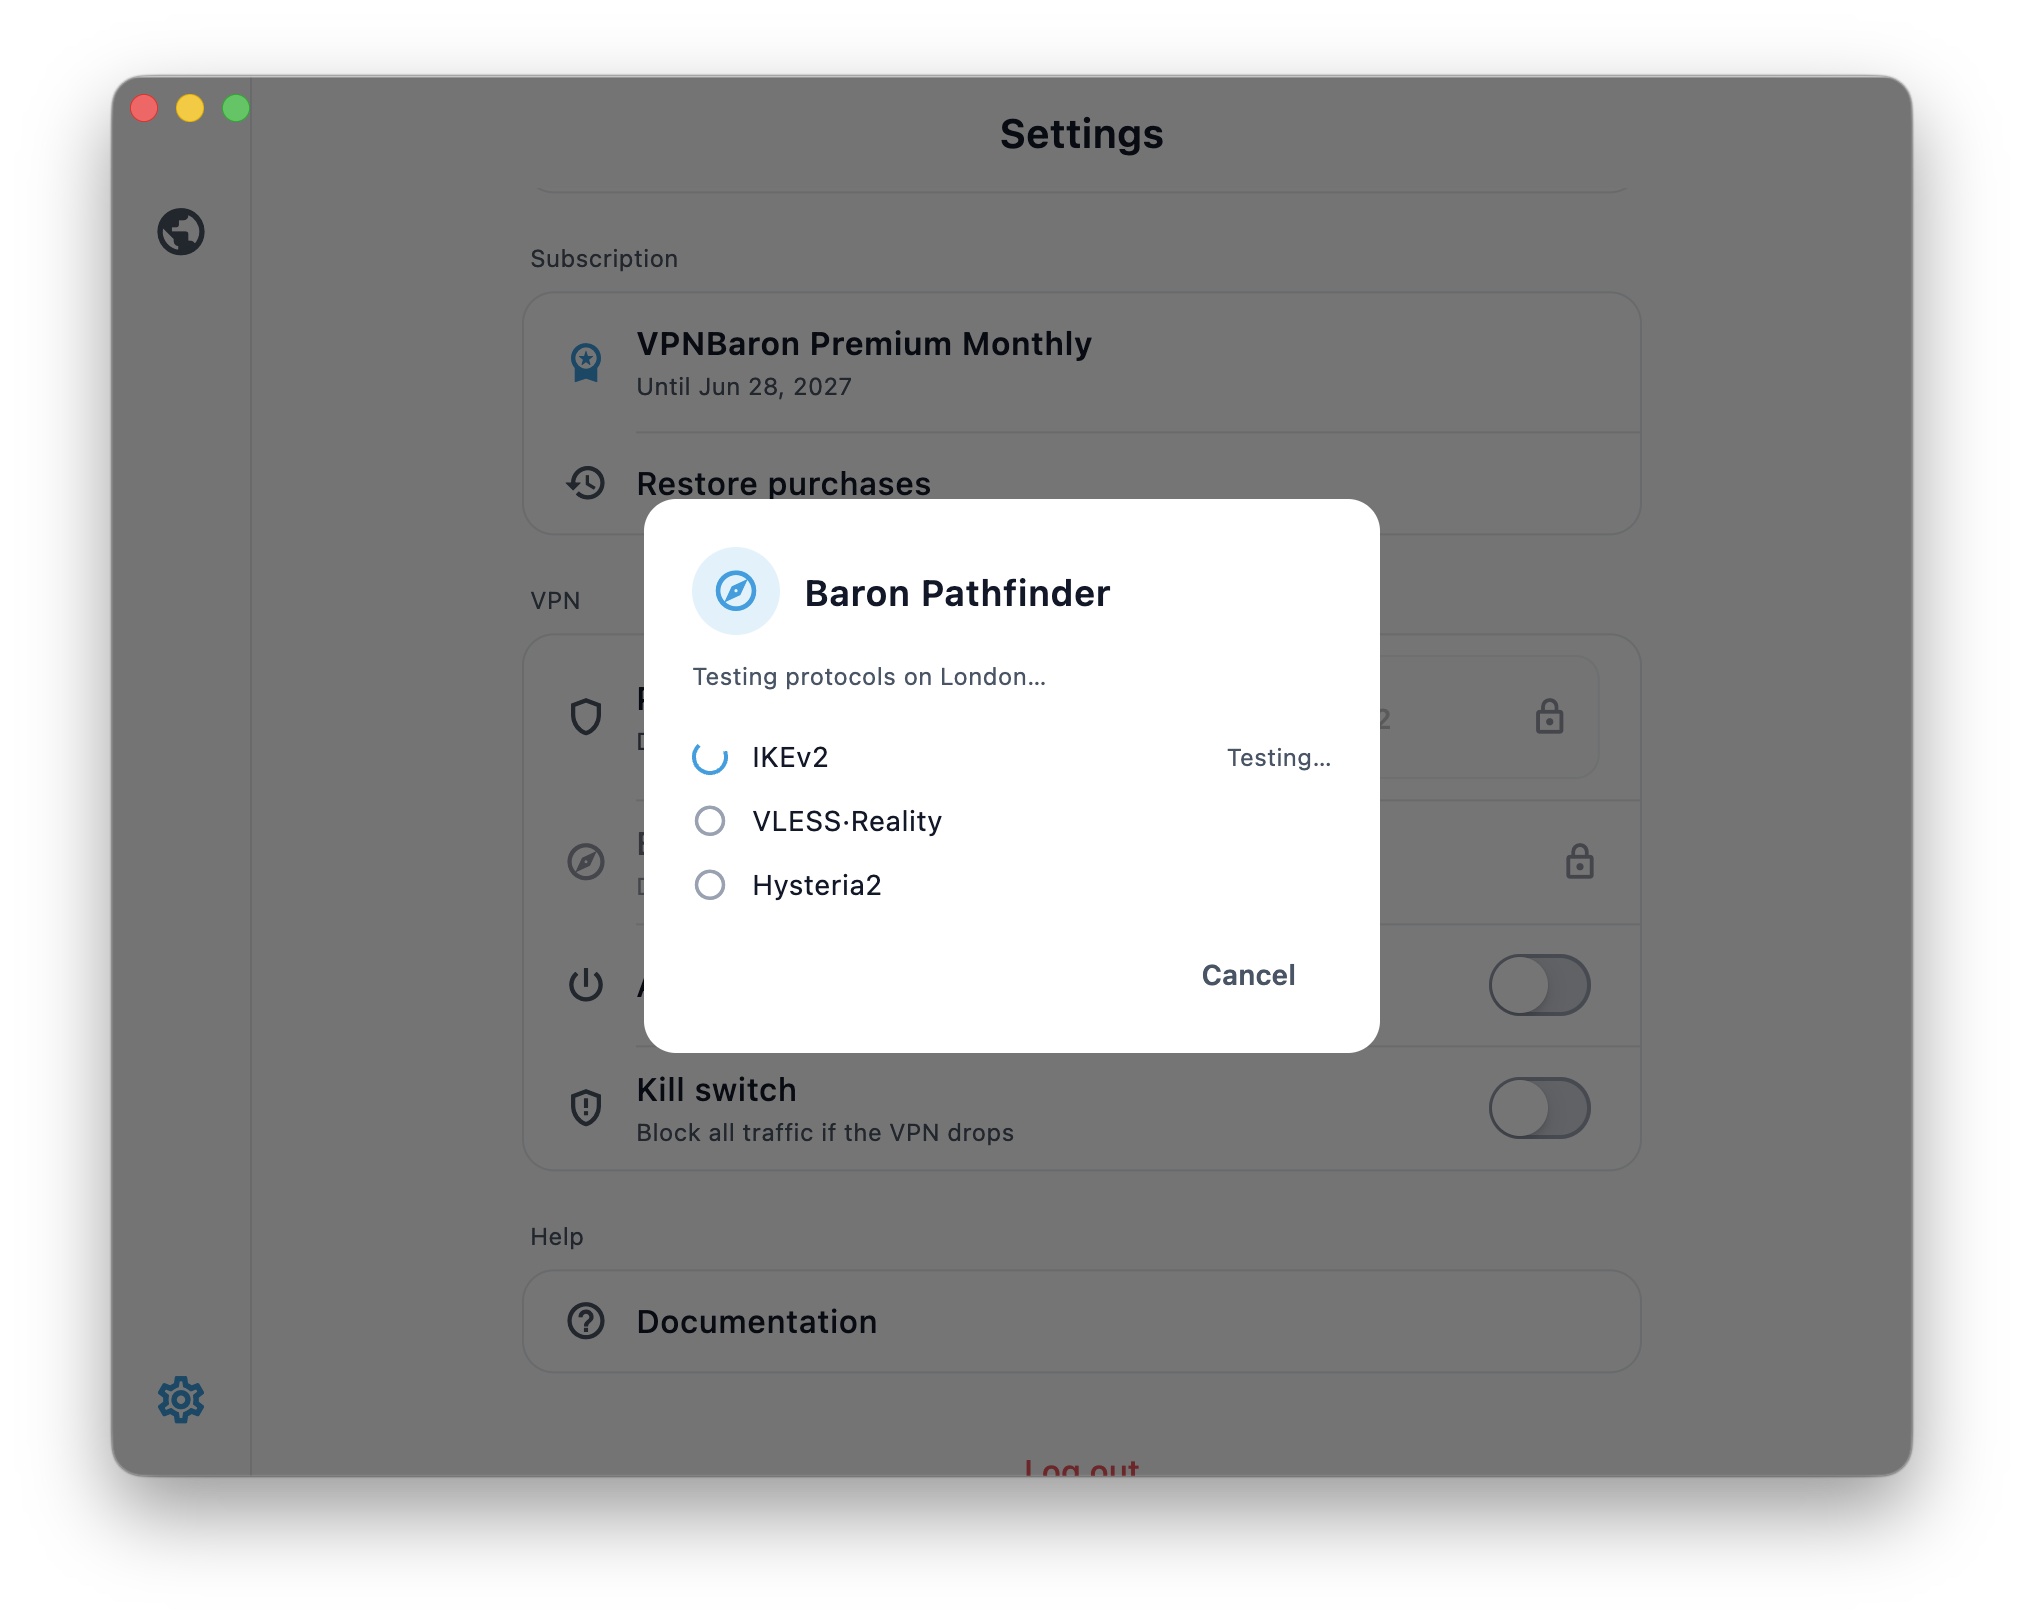
The app route replaces all of that with one decision. In the VPNBaron app, Baron Pathfinder tests routes on the network you’re standing on and picks what connects, falling back to Reality when the network fights.
Fresh server addresses ship to everyone the day they go live, so a blocklisted IP is our rotation problem, not your evening project.
VPNBaron
Retire your Shadowsocks box
Reality and Hysteria2 on every location, one subscription for your existing client or one tap in ours. Enough time to test it on the exact network that’s cutting you off.
FAQ
Is Shadowsocks still safe to use in 2026? On lenient networks, yes. Against modern equipment it’s increasingly fragile: entropy-based flagging and active probing both hit it, and both are exactly what Reality was designed to survive.
Does Shadowsocks still work in China? Intermittently. Plain Shadowsocks tends to get cut fast, especially around sensitive dates. Plugin setups last longer but share the same exposure.
Is VLESS Reality faster? They’re close on clean networks; Reality pays a small camouflage cost, Shadowsocks is marginally leaner. The real question is which one still connects on a hostile network, and there Reality wins.
Do I need new apps to switch? Usually not: V2Box, Hiddify and Clash Meta speak both. It’s a subscription swap, not a toolchain swap.
What about Shadowsocks with plugins (v2ray-plugin, obfs)? They extend its life by dressing it as WebSocket or TLS. You’re maintaining by hand the disguise Reality ships natively, without fully solving active probing.
Related guides
- VLESS Reality protocol
- Hysteria2 vs VLESS Reality: which one and when
- Trojan vs VLESS Reality
- What deep packet inspection actually does
More in VPN protocols·Related: Stealth VPN